Service 11 / 12
IT Compliance & Risk Management
Technical safeguards, policies and documentation for regulated practices — dental, medical, legal, financial and retail.
HIPAA, PCI and insurance requirements translated into a checklist we handle.
Regulations like HIPAA and PCI DSS describe outcomes, not products, which leaves practice owners guessing what they actually need. We translate the requirements into concrete technical controls, put them in place and keep the evidence organised.
When an auditor, insurer or client security questionnaire arrives, you have current documentation instead of a scramble.
What’s included
Compliance, done properly.
- 01HIPAA security risk assessments for medical and dental practices
- 02PCI DSS scoping and controls for businesses taking card payments
- 03Written IT policies: acceptable use, access, incident response
- 04Encryption, access logging and audit trails
- 05Vendor and business-associate documentation support
- 06Annual review and evidence binder for audits
How it works
- 01
Assess
Gap assessment against the standard that applies to you.
- 02
Remediate
Technical fixes and written policies, prioritised by risk.
- 03
Maintain
Annual reviews, staff training and ongoing evidence.
What changes
What you’ll notice.
- Confidence when an auditor or insurer asks questions
- Patient and customer data protected by design
- Policies your staff actually understand
They found we were paying for nine Microsoft licences for people who had left. That alone covered a good part of the first month.
Questions
Compliance FAQ
01Can you make us ‘HIPAA certified’?
There is no official HIPAA certification. We help you meet the Security Rule’s requirements and document that you have done so.
02We use a cloud practice-management system. What else do we need?
The software vendor covers their platform; you remain responsible for devices, accounts, Wi-Fi and staff access. That is where we help.
03Do you provide legal advice?
No. We handle the technical controls and documentation, and work alongside your attorney or compliance officer where needed.
Often paired with
 Cybersecurity & Threat ProtectionLayered protection sized for a small business, not a bank.
 Data Backup & Disaster RecoveryBackups you’ve actually tested, and a plan for the bad day.
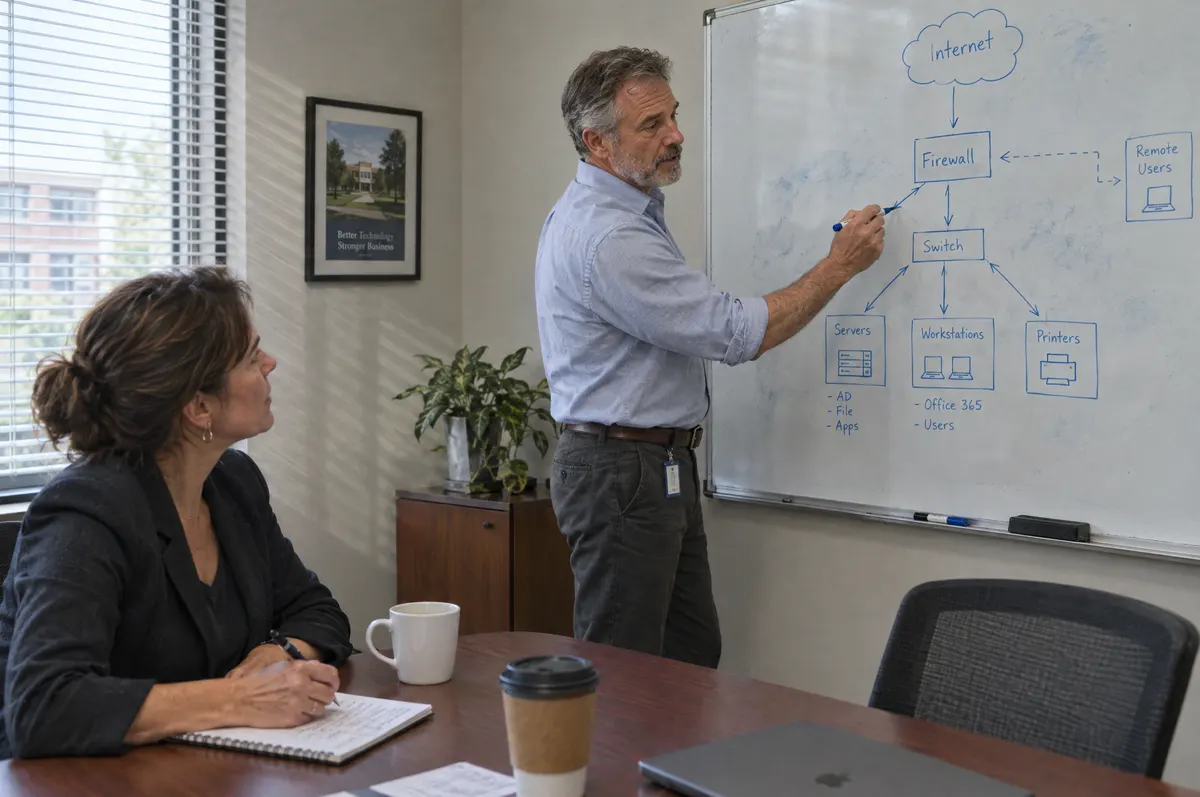 IT Consulting & vCIO StrategySenior technology advice without a full-time executive salary.
Free IT assessment
Ready for compliance you don’t have to think about?
A free assessment takes about an hour on site. You get a written summary of what’s working, what’s at risk and what we’d fix first — whether or not you hire us.
Book your free assessment